

WordPress 7.0 Security Updates Explained
 Suyash Raizada
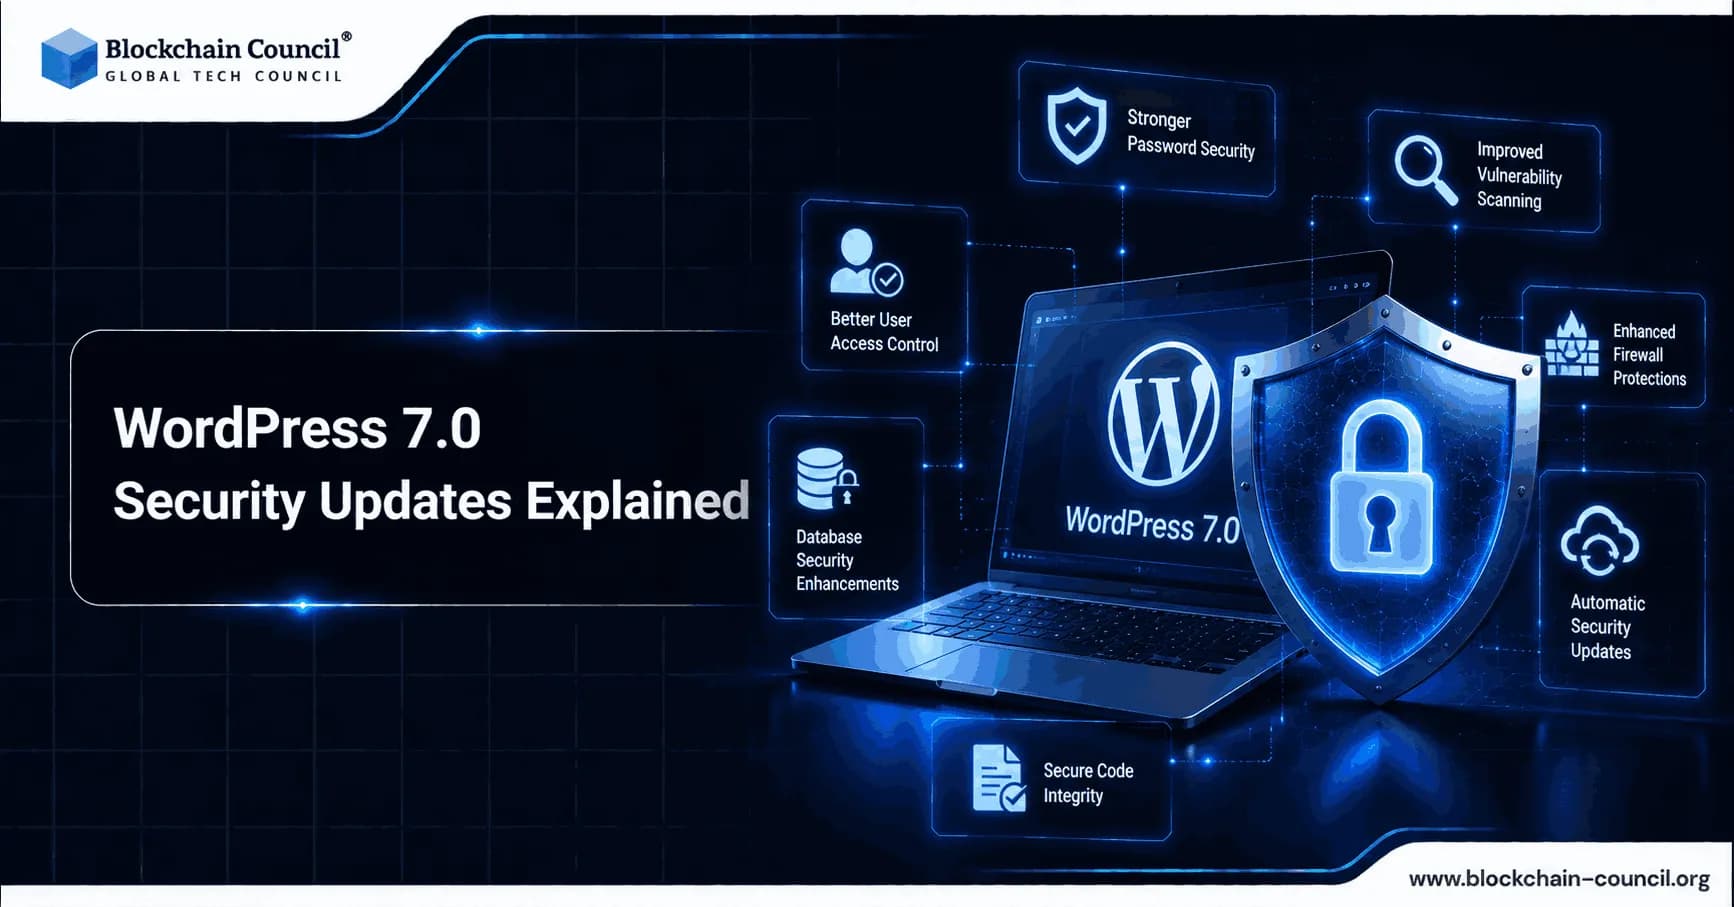
WordPress 7.0 security updates are shaping this release into more than a feature refresh. They signal stricter infrastructure requirements, new core interfaces, and editor architecture changes that can materially affect your security posture. For administrators and developers, the key risk is not only what WordPress 7.0 changes in core, but how those changes interact with PHP versions, plugins, and custom code. A safe upgrade requires planning, testing, and hardening - not a one-click update. For professionals developing AI-enabled applications and workflows, a Certified Artificial Intelligence (AI) Developer certification can also help build a stronger understanding of AI development concepts and implementation practices.
What is changing in WordPress 7.0 from a security perspective?
Based on public release-track reporting across hosting providers and the WordPress ecosystem, WordPress 7.0 is widely described as a modernization release that affects security in three primary ways: a higher PHP baseline, new or expanded core interfaces (including capability and AI-related surfaces), and editor changes that can break assumptions in themes and plugins. As AI becomes a more prominent part of WordPress workflows, understanding how to secure AI-enabled systems is equally important. A Certified AI Security Professional can develop specialized knowledge around protecting AI systems, managing security risks, and addressing threats that can emerge when AI is connected to applications and data.

1) PHP baseline increases: minimum PHP 7.4, newer versions recommended
Multiple ecosystem sources report that WordPress 7.0 raises the minimum supported PHP version to PHP 7.4, with PHP 8.2+ or newer versions commonly recommended for security and performance. Operationally, this means:
Sites on PHP 7.2 or 7.3 should expect upgrade blockers or update friction.
Running unsupported PHP versions increases exposure to unpatched runtime vulnerabilities, which directly undermines CMS hardening efforts.
Plugin and theme compatibility risks increase during the transition period, particularly for older codebases that relied on legacy PHP behavior.
The security upside of raising minimum PHP versions is reduced legacy exposure and encouragement of modern security practices - for example, using supported libraries and current cryptographic and HTTP stacks. The downside is that rushed migrations can introduce misconfigurations and outages if not staged properly.
2) New core interfaces and AI-related connectors broaden the attack surface
Several reports mention new or expanded core capabilities such as an Abilities API and unified AI interfaces or connectors. Any new integration surface can create fresh failure modes if permissions and trust boundaries are not clearly defined. For WordPress security, the recurring risks include:
Over-permissioned plugins that request broad capabilities to access new APIs.
Misconfigured permission checks on REST endpoints and admin actions.
AI workflow risks such as prompt injection patterns, unsafe tool invocation, or accidental leakage of privileged context when admin data is included in prompts.
The practical implication: treat new interfaces as secure only when implemented securely. Assume any new API is a potential escalation path until proven otherwise through testing and review.
3) Editor and block changes can cause security regressions indirectly
WordPress 7.0 is also described as delivering meaningful editor architecture changes, including iframes in the editor by default and block-related updates such as block binding changes. These are not inherently vulnerabilities, but they can break admin UI scripts and custom editor extensions. When teams apply quick compatibility patches, common security mistakes tend to follow:
Skipping capability checks to get functionality working in the new editor context
Relaxing sanitization or validation under deadline pressure
Adding new REST routes without proper authentication and permission callbacks
Editor shifts can become a catalyst for insecure hotfixes unless you plan a staged migration and allocate time for secure refactoring.
Why plugin risk still dominates WordPress security
Even with stronger core baselines, real-world WordPress incidents frequently originate with plugin vulnerabilities. Recent vulnerability roundups have highlighted multiple high-risk plugin flaws, including privilege escalation, authentication bypass and account takeover, and SQL injection, with severity ratings ranging from CVSS 7.5 up to 10.0. Some cases have been described as actively exploited in the wild, illustrating how quickly attackers operationalize public disclosures.
This aligns with ongoing guidance from major WordPress security vendors and managed hosting providers: the most effective defenses are patch speed and attack surface reduction.
Release timing and why it matters for security planning
WordPress core communications reported a schedule update moving the WordPress 7.0 release date to May 20, 2026. When major releases shift, many teams end up running longer parallel tracks:
More time spent maintaining staging environments
Extended periods of compatibility uncertainty for plugins and themes
Greater likelihood that admins postpone updates and accumulate patch debt
The security takeaway: use schedule changes to extend testing and hardening, not to delay preparation. Update readiness should be continuous, not tied to a single release date.
Hardening checklist for WordPress 7.0 admins
Admin-side hardening focuses on reducing exposure and tightening operational discipline. The following checklist applies to most small business and enterprise WordPress environments.
1) Upgrade PHP first and validate hosting compatibility
Before updating to WordPress 7.0, move to PHP 8.2+ where feasible, or at minimum PHP 7.4. Confirm:
Opcode cache and server modules are compatible
Database and TLS configurations meet your security baseline
Backup jobs, cron, and caching layers still operate as expected
2) Inventory plugins and remove what you do not need
Every plugin expands your attack surface, even inactive ones. Prioritize removing plugins that:
Touch authentication, registration, password reset, or account recovery
Handle payments, checkout, or order data
Accept file uploads or manipulate media
Are abandoned or rarely updated
Duplicate core WordPress features
Teams responsible for plugin governance and secure administration can benefit from cybersecurity-oriented training that reinforces vulnerability management and secure configuration concepts.
3) Define patch SLAs based on severity
Given how quickly exploit attempts can follow public disclosures, implement a clear SLA model:
Critical plugin vulnerabilities: patch within hours, same day when possible
High severity issues: patch within 24 to 72 hours
Medium and low severity: patch in the next scheduled maintenance window
Back this up with asset inventory, automated alerting, and a change-control path for emergency plugin updates.
4) Enforce multi-factor authentication (MFA) for all admins
MFA reduces the impact of stolen credentials and makes account takeover harder when attackers target login flows. Apply MFA to:
All administrator accounts
Editors with publishing permissions in high-traffic environments
Any account with access to plugins, themes, or site settings
5) Use staging for the WordPress 7.0 migration
Clone production to staging and test:
Theme rendering and critical templates
Checkout flows, forms, membership logic, and transactional emails
REST API consumers and webhooks
Admin workflows and custom dashboards
Scheduled tasks and third-party integrations
Then deploy with a rollback plan and a defined monitoring window.
6) Back up and test restores, not only backups
Verify that you can restore both database and files. Confirm you can rebuild the site on clean infrastructure if needed. Tested restores are a security control because they reduce downtime and remove the pressure to keep a compromised environment online.
7) Restrict admin access and apply least privilege
Minimize the number of administrator accounts
Use IP allowlisting for /wp-admin where it fits your operating model
Audit roles and capabilities on a regular schedule
Disable XML-RPC if it is not required by your integrations
Hardening checklist for WordPress 7.0 developers
Developer-side hardening is about ensuring your code remains secure under new runtime expectations and editor architecture changes.
1) Audit custom code and dependencies for PHP compatibility
With a higher PHP baseline, review:
Deprecated functions and legacy libraries
Composer dependencies and transitive packages
Custom plugins and mu-plugins that assumed older PHP behavior
Do not treat "it runs" as "it is safe." Compatibility patches are a frequent source of new injection and authorization bugs.
2) Re-test editor integrations under iframe and block changes
If your code manipulates editor internals, revalidate:
Event handlers and selector logic
PostMessage and cross-context communication patterns
Any admin-side script that assumes direct DOM access
3) Validate capability checks and nonce handling everywhere
For every endpoint and action:
Use current_user_can() checks that match the sensitivity of the action
Require and validate nonces for all state-changing requests
Implement permission callbacks for REST routes
Fail closed when permission checks are ambiguous
4) Treat AI inputs and outputs as untrusted data
If your WordPress stack uses AI connectors or content assistants, apply the following assumptions:
Malicious prompts can attempt to override instructions
Injected content may include unsafe HTML, links, or scripts
Tool invocation can be abused if privileged actions are exposed
Sanitize AI outputs, restrict what data is sent externally, and avoid placing admin secrets or privileged context into prompts. Teams building AI-enabled CMS workflows can benefit from AI security-focused training to support safer design and governance practices.
5) Use secure defaults for custom blocks and plugins
Whitelist allowed HTML where possible
Validate and sanitize all block attributes
Lock down upload endpoints and enforce file type validation
Log privileged actions to support incident response
6) Automate security testing in CI
To prevent regressions during the WordPress 7.0 transition, include:
Static analysis for PHP and JavaScript
Dependency and vulnerability scanning
Integration tests for authentication and authorization flows
Regression tests for sanitization and output escaping
Governance considerations for enterprises and regulated teams
If your organization follows ISO 27001, SOC 2, or applicable privacy regulations, treat the WordPress 7.0 migration as a controlled change event:
Access control: document roles, admin account counts, and MFA enforcement
Vulnerability management: track plugin inventories and patch timelines
Third-party risk: review plugin vendors and their update cadence
Data protection: understand what personally identifiable information is collected through forms and membership systems
AI governance: document external data sharing and model or tool access boundaries
Maintain evidence: keep staging test records, rollback plans, and update logs as part of your change management documentation.
AI Microdrama and Emerging AI Applications
One emerging application is AI microdrama, where generative AI helps bring serialized stories, characters, and fictional worlds to life. As generative AI expands into content creation and digital experiences, applications such as AI microdrama demonstrate how AI can support new forms of storytelling while creating additional considerations around security, data handling, and third-party integrations.
For professionals working with modern websites and emerging technologies, developing broader technical knowledge can also be valuable. A Tech Certification can complement WordPress security expertise by helping professionals build familiarity with emerging technology concepts and their practical applications.
Conclusion: treat WordPress 7.0 as a security project, not a routine update
WordPress 7.0 security updates represent a shift in baseline expectations: newer PHP requirements, new core interfaces, and editor architecture changes that can invalidate old assumptions. The safest upgrade path follows consistent principles for both admins and developers:
Modernize PHP before upgrading
Reduce plugin exposure
Patch fast with defined SLAs
Enforce MFA and least privilege
Test in staging with rollback readiness
Audit custom code and automate security testing
Handled with this level of discipline, WordPress 7.0 becomes an opportunity to strengthen operational security and resilience - not just another version increment.
For teams managing technology-focused websites, security and development are only part of the broader digital ecosystem. Understanding how to communicate, position, and grow technology products can complement technical expertise, making a Marketing Certification a useful additional learning path for professionals working across digital and technology-focused environments.
FAQs
1. What security updates were released for WordPress 7.0?
The WordPress 7.0 branch has received multiple security releases since its May 2026 launch. WordPress 7.0.2 addressed a critical SQL injection issue and a REST API issue that could lead to remote code execution, while 7.0.3 addressed multiple XSS, privilege escalation, information disclosure, SSRF, and other vulnerabilities.
2. What is the latest WordPress 7.0 security release?
WordPress 7.0.4 is the latest 7.0 branch release listed in the WordPress release archive as of August 12, 2026. It contains a security fix for an authenticated Author+ remote code execution vulnerability involving malicious file uploads on sites using Imagick and Ghostscript.
3. Why should WordPress 7.0 sites be updated immediately?
Security vulnerabilities can become easier to exploit after details about a patched issue become public. WordPress recommends keeping core, themes, and plugins updated because outdated software can leave known vulnerabilities available to attackers.
4. Does updating WordPress 7.0 make a website completely secure?
No. An update fixes known issues in the affected software, but website security is a continuous process. Hosting configuration, plugins, themes, user accounts, passwords, file permissions, backups, and application code can all introduce additional risks.
5. How can administrators harden a WordPress 7.0 website?
Start by keeping WordPress, plugins, themes, PHP, and the hosting environment current. Use strong unique passwords, enable two-factor authentication, limit administrative access, maintain reliable backups, use trusted extensions, and consider WAF or CDN protection.
6. Should WordPress administrators enable two-factor authentication?
Yes. Two-factor authentication adds another authentication factor beyond a password and can significantly reduce the impact of stolen credentials. WordPress recommends 2FA for administrator accounts, typically through a reputable plugin or identity provider.
7. Are strong passwords enough to protect WordPress?
No. Strong, unique passwords are important, but they should be combined with 2FA, access controls, rate limiting, monitoring, and timely updates. A password alone cannot protect an account if credentials are compromised through phishing or another attack.
8. How can developers protect WordPress plugins from security vulnerabilities?
Developers should validate and sanitize input appropriately, escape output, use WordPress APIs and permission checks correctly, protect sensitive actions with nonces where appropriate, and avoid unnecessary direct database queries. Code should also be tested against current WordPress and PHP versions and reviewed for common vulnerabilities such as SQL injection and cross-site scripting.
9. How important are plugin and theme updates for WordPress security?
They are extremely important because vulnerabilities can exist outside WordPress core. WordPress specifically recommends keeping plugins and themes updated and choosing extensions that are actively maintained.
10. Should unused WordPress plugins and themes be removed?
Yes. Removing extensions that are no longer needed reduces the amount of software that needs to be maintained and can reduce potential attack surfaces. Deactivating an unused plugin is not always equivalent to removing it, so administrators should follow the extension's intended removal process.
11. How can administrators protect WordPress against brute-force attacks?
Use strong unique passwords and 2FA, rate-limit login attempts, and consider WAF or CDN-based protection. CAPTCHA or similar anti-bot controls can also help, while monitoring authentication activity can identify suspicious login patterns.
12. Should XML-RPC be disabled in WordPress?
If a site does not need XML-RPC, administrators can consider disabling or restricting it. If XML-RPC is required, WordPress recommends protecting and rate-limiting it rather than treating simple obscurity as the primary security measure.
13. How can a Web Application Firewall improve WordPress security?
A WAF can inspect incoming web traffic and block certain malicious requests before they reach the WordPress application. This can provide an additional layer against attacks such as automated abuse and suspicious requests, although a WAF should complement rather than replace secure application development and updates.
14. Why are WordPress backups important for security?
Backups provide a recovery mechanism if a site is compromised, corrupted, or otherwise damaged. WordPress recommends maintaining trusted backups of the site's files and database and having a recovery plan rather than assuming prevention alone will eliminate all security risk.
15. How should developers handle file uploads securely in WordPress?
Developers should validate file types, enforce appropriate permissions and size restrictions, avoid unnecessary executable uploads, and use WordPress's established media and validation mechanisms where appropriate. The 7.0.4 security release demonstrates why file-upload handling and related server components can have serious security implications.
16. What security issues should WordPress developers watch for in the REST API?
Developers should carefully validate REST API input, enforce authorization and capability checks, use appropriate schemas, and avoid exposing sensitive information unnecessarily. WordPress 7.0.2 included a REST API batch-route confusion and SQL injection vulnerability that could lead to remote code execution, highlighting the importance of secure API implementation.
17. How can developers reduce XSS risks in WordPress 7.0?
Treat user-controlled data as untrusted and escape output for the appropriate context. Developers should use WordPress's sanitization and escaping APIs correctly and carefully review custom blocks, administrative interfaces, REST endpoints, and other components that process user-generated content.
18. Does WordPress 7.0 require a specific PHP version for security?
WordPress 7.0 has a minimum supported PHP version of 7.4, while WordPress currently recommends PHP 8.3 or newer. Developers should test plugins and themes against supported PHP versions and keep the server's PHP installation maintained.
19. What should developers test after a WordPress 7.0 security update?
Test authentication, forms, media uploads, REST API functionality, custom plugins, themes, integrations, scheduled tasks, and important frontend and administrative workflows. A staging environment is preferable for testing significant changes before deploying them to production.
20. What is the best WordPress 7.0 security hardening strategy?
Use a layered approach: keep core, plugins, themes, and PHP updated; enforce strong authentication and 2FA; minimize user privileges; remove unnecessary extensions; protect login and API endpoints; use trusted hosting and WAF controls; monitor the site; and maintain tested backups. WordPress emphasizes that security is about reducing risk and preparing for recovery, not achieving perfect security.
Related Articles
View All
AI & ML
Meta Launches Muse Wonder: Its New AI Model Explained
Meta has launched Muse Wonder and Muse Wonder Full, new AI models built for personal and professional agents. Learn the features, pricing, access options and how they compare with rivals.
AI & ML
AI Explained: From Machine Learning to Generative AI
AI Explained in simple terms. Learn the differences between AI, machine learning, and deep learning, how neural networks and LLMs work, and how generative and multimodal AI create content.
AI & ML
NVIDIA Cosmos 3 Explained: The Next Generation of Physical AI
Explore NVIDIA Cosmos 3, an open foundation model for Physical AI that combines vision reasoning, world simulation, multimodal generation, and action prediction for robotics and autonomous systems.
Trending Articles
The Role of Blockchain in Ethical AI Development
How blockchain technology is being used to promote transparency and accountability in artificial intelligence systems.

Top 5 DeFi Platforms
Explore the leading decentralized finance platforms and what makes each one unique in the evolving DeFi landscape.
How to Install Claude Code
Learn how to install Claude Code on macOS, Linux, and Windows using the native installer, plus verification, authentication, and troubleshooting tips.