Ethical Hacking for AI Systems: Step-by-Step Pen-Testing for ML and LLM Apps
Learn a step-by-step ethical hacking methodology for AI systems, including pen-testing ML pipelines and LLM apps for prompt injection, RAG leaks, and tool abuse.
Browse the latest ai articles, tutorials, and research from Blockchain Council.(1848 articles)
Learn a step-by-step ethical hacking methodology for AI systems, including pen-testing ML pipelines and LLM apps for prompt injection, RAG leaks, and tool abuse.
Learn how AI threat detection in SOCs uses ML anomaly detection to spot unknown threats while managing risks like false negatives, alert fatigue, and over-reliance on automation.
Learn how to build an AI incident response plan with monitoring, triage, containment, and postmortems to reduce MTTR, cut false positives, and improve recovery.
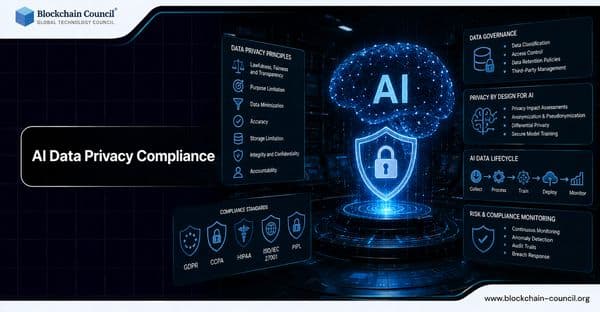
AI data privacy compliance in 2026 blends GDPR, HIPAA, and the EU AI Act with expanding state laws. Learn how to implement inventories, DPIAs, BAAs, and human oversight.
Compare privacy-preserving AI techniques: differential privacy, federated learning, and secure enclaves. Learn trade-offs, use cases, and hybrid best practices.
Learn secure retrieval-augmented generation (RAG) defenses against data leakage, poisoned sources, and hallucination exploits across ingestion, retrieval, and generation.
Learn a practical LLM security testing playbook using red teaming, eval harnesses, and safety regression tests to catch jailbreaks, leakage, and bias in CI/CD.
Prompt injection and LLM jailbreaks can bypass guardrails and compromise agent workflows. Learn practical layered defenses for secure generative AI systems.
Learn AI security in finance with practical fraud detection hardening, model risk management controls, and compliance-ready audit trails for modern regulators.
Model theft and extraction in 2026 threatens LLM intellectual property and user privacy through API probing, inversion attacks, and distillation. Learn how these attacks work and how to build layered defenses to reduce risk.
AI security in healthcare requires protecting PHI, hardening clinical models against manipulation, and enforcing safety with monitoring, governance, and secure-by-design controls.
Learn a practical blueprint for secure AI systems using zero-trust design, least-privilege IAM, AI gateways, segmented AI zones, and lifecycle governance.